

Before you start
You need integration-management permission, authorized provider credentials and access to the companies you intend to synchronize. Ticket configuration can additionally require Ticket Settings permission. Keep credentials in the connection form and your approved secret store. In ConnectWise PSA, create an active API member under System > Members > API Members with a dedicated security role. In its API Keys tab, add a named key and save it; securely retain both keys because the private key is shown only when created. Use the API hostname for your region, such asna.myconnectwise.net, and your ConnectWise Company ID. The vendor API-member instructions show key creation; use MSPortal’s permission results for the capabilities you intend to enable, rather than copying another integration’s role wholesale.
Connect the provider
- Open Settings > Integrations, find ConnectWise Manage, and open setup. Use Configure for the existing connection.
- Enter API URL, Company ID, Public Key and Private Key.
- Select Test Connection when ready to connect. For a new connection, a successful test also creates and saves the integration. There is no separate Create Integration button in this PSA wizard.
- Review the result and continue to Permissions. An existing connection can initialize with a Connected indicator; that is not proof of a fresh test.
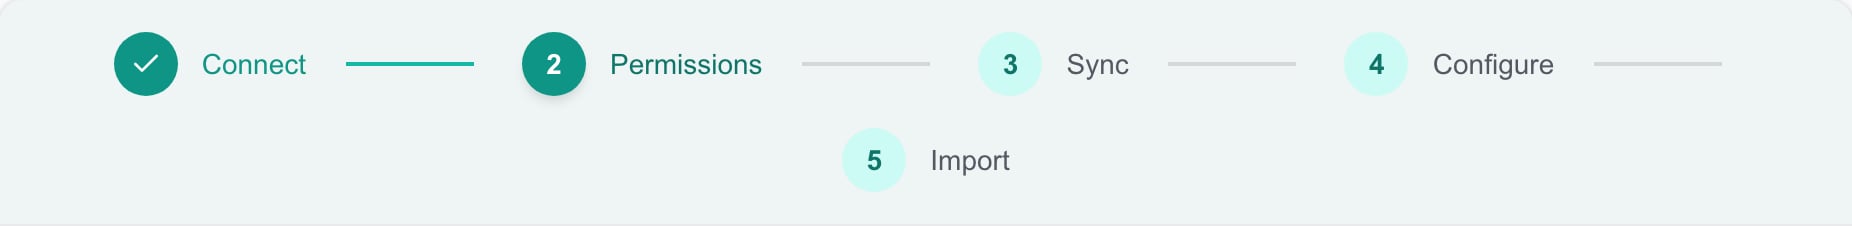
MSP example: the setup steps for an existing connection. The Connect checkmark does not represent a new test.
Check permissions
The permission screen checks vendor endpoints and reports required access, optional access and unavailable or unverified results. Required denied access prevents the supported progression. A denied optional sync permission keeps its corresponding sync off. Checklist write permissions are checked separately and do not turn off project synchronization. Read the reported failure before changing the API role. A timeout, unavailable endpoint or unverified check is not automatically proof of a missing permission. Retry after resolving the actual problem. Sync checks exercise read access. The Project checklist writes check also reads the connected API member’s own security settings to verify Project Ticket Tasks Add, Edit and Inquire access. It does not create or change a checklist item. A granted result confirms those role levels; it does not guarantee every write will succeed or verify project creation, project/ticket status changes, phase edits, comments, time entries, checklist deletion or warranty updates.Project management permissions
Configure the API member that owns MSPortal’s configured keys for the project work your staff will perform. Open System > Members > API Members, check its assigned role, then edit that role under System > Security Roles. Your staff member’s personal ConnectWise role does not grant access to the integration. The following is the recommended project read/create/update configuration. All allows the API member to work across the intended projects; My can prevent an integration account from updating work assigned to someone else. Keep company, location and business-unit access aligned with the records you intend to manage.
For ticket status changes across your managed projects, configure Project Tickets → Edit Level: All. Granting Project Ticket Tasks Edit alone only covers checklist changes. If ordinary status changes work but closing fails, review Close Project Tickets or Close Projects, as appropriate.
Supporting access
Project management also uses records outside the Project module. Retain the connection wizard’s required company, contact, member and lookup read permissions, and configure these for the features you use:
These permissions support the operations above; they do not override ConnectWise validation, board restrictions, closed-record rules or missing required fields. Use the ConnectWise security-role documentation for your version’s role controls.
Delete access and local project work
Read/create/update workflows do not require blanket Delete permissions. To use Delete checklist item where available, additionally grant Project → Project Ticket Tasks → Delete Level: All. MSPortal checks that permission separately; an unreadable or unverified role does not enable deletion. Leave Delete disabled on unrelated project records. MSPortal-only projects, reusable portal templates and portal project registers use MSPortal permissions. An explicit action that creates or updates a PSA project, phase or ticket needs the vendor permissions above. Granting vendor access does not grant a staff or client user access inside MSPortal.Allow project checklist changes
Adding a checklist item or changing its completion state writes to ConnectWise using the API member that owns the integration’s configured keys. The staff member needs the appropriate MSPortal project permission, and the API member separately needs ConnectWise access. Changing the staff member’s personal ConnectWise role does not change the integration’s permissions.- In ConnectWise, open System > Members > API Members and identify the member that owns the public key configured in MSPortal.
- Check that member’s assigned security role, then open it under System > Security Roles.
- Expand Project and review Project Ticket Tasks:
Keep the role dedicated to MSPortal. If it is shared with another integration, review the effect on that integration before changing it. Checklist creation and completion do not require granting Delete access. Deleting an item has the separate requirement described above.
After saving the role, return to Settings > Integrations > ConnectWise Manage > Configure > Permissions and select Re-check. The Project checklist writes result is separate from Projects:
- Granted: all three task permission levels are All.
- Not permitted: the role explicitly denies at least one required task permission.
- Could not verify: the role settings could not be read or interpreted, or access is scoped to My and cannot establish access to every intended ticket. Review the role and ticket scope in ConnectWise; this result does not prove the action is denied.
A green Projects read check can coexist with denied checklist writes. For example, Project Ticket Tasks with Inquire Level All and Add/Edit Level None allows viewing the checklist but blocks additions and completion changes. Project synchronization can remain enabled while you correct those write permissions.
Select synchronization scope
Select the intended service boards and excluded ticket statuses. Review company type/status filters and the supported opportunity, project, invoice, product catalog and change-management options. A company excluded by synchronization filters will not be made available merely by changing its portal mapping. Review filters before continuing. Synchronizing source records, linking them to companies and importing portal records are separate steps. Automatic company/contact import options can create portal records when matching source records arrive. Review any import preview and the selected categories carefully; do not rely on a confirmation appearing for every save. Proceeding from Sync saves the selected scope and starts background synchronization. Options in later steps may remain incomplete while it runs. Check errors and the connection’s actual sync result before treating an empty list as the final dataset. Warranty writeback is an optional vendor write. Enable it only when you intend resolved warranty data to update the connected PSA records.Configure portal behavior
Configure closed statuses and client-comment status for the selected boards, then review the resolution status groups. Configure opportunity stages/types/probabilities and invoice settings where enabled. Use Resync PSA settings when newly created vendor boards or statuses are missing. Configuration forms save changes automatically after editing. Wait for the saved state; wizard navigation waits for pending saves and reports failures. Leaving the screen is not a substitute for checking a failed save. Ticket defaults additionally require Ticket Settings permission. Quick Sync requests ticket synchronization. Clear & Resync clears portal ticket data for this connection before reloading it. Use the latter only for an intended rebuild, and check the subsequent result; it is not a harmless refresh.Import and finish
The Import step offers Users, Companies and Locations. Review the parent company before linking a location. Review existing portal records before creating duplicates. Company links determine which client can see synchronized data. Apply the intended company and user selections and check the result. Complete Setup also attempts to apply pending company/user imports before completing the wizard. It can start background work, so setup completion is not proof that every import or sync succeeded. An import-page link only navigates to that workflow. Use Save & Exit to save wizard progress when pausing. Reopen the connection to continue and verify the saved state. Portal invitations and client permissions remain separate from discovering provider contacts.Maintain the connection
Reopen setup to inspect scope and errors. A successful retest of changed fields is not proof of credential rotation: this wizard has no separate update-credentials action. Confirm the supported replacement path before revoking working vendor credentials. Delete Integration opens a named confirmation. Confirm Delete only to remove the connection and its associated settings; cancel preserves it. Vendor-side credential revocation is separate.Troubleshooting
Frequently asked questions
Does Test Connection only test credentials?
Does Test Connection only test credentials?
For a new connection, a successful test also creates the integration. Enter credentials only when you intend to connect it.
Does a green permissions result verify ticket writes?
Does a green permissions result verify ticket writes?
Not every write. Sync checks probe read access, while Project checklist writes reads the API member’s task permission levels without changing data. Creating tickets, comments or other vendor changes still needs the relevant write permission and a successful action.
Does Complete Setup mean all data is ready?
Does Complete Setup mean all data is ready?
No. Check the background sync result and verify company, user and device imports separately.
Will every discovered contact receive portal access?
Will every discovered contact receive portal access?
Discovery and import are separate. Review user matches, company links and the permissions assigned to portal users; invitation is a separate workflow.
Can I replace saved credentials by retesting the form?
Can I replace saved credentials by retesting the form?
Do not treat a successful retest as proof that replacement credentials were saved. This wizard does not provide a separate credential-update action; confirm the supported update path before revoking the old credential.