

Choose a starting point
Open Settings > Compliance > Playbooks. Best Practices groups operational and technology reviews. Security Frameworks includes the available CIS benchmark catalog and framework families such as NIS2. Search by name or description when you already know what you need.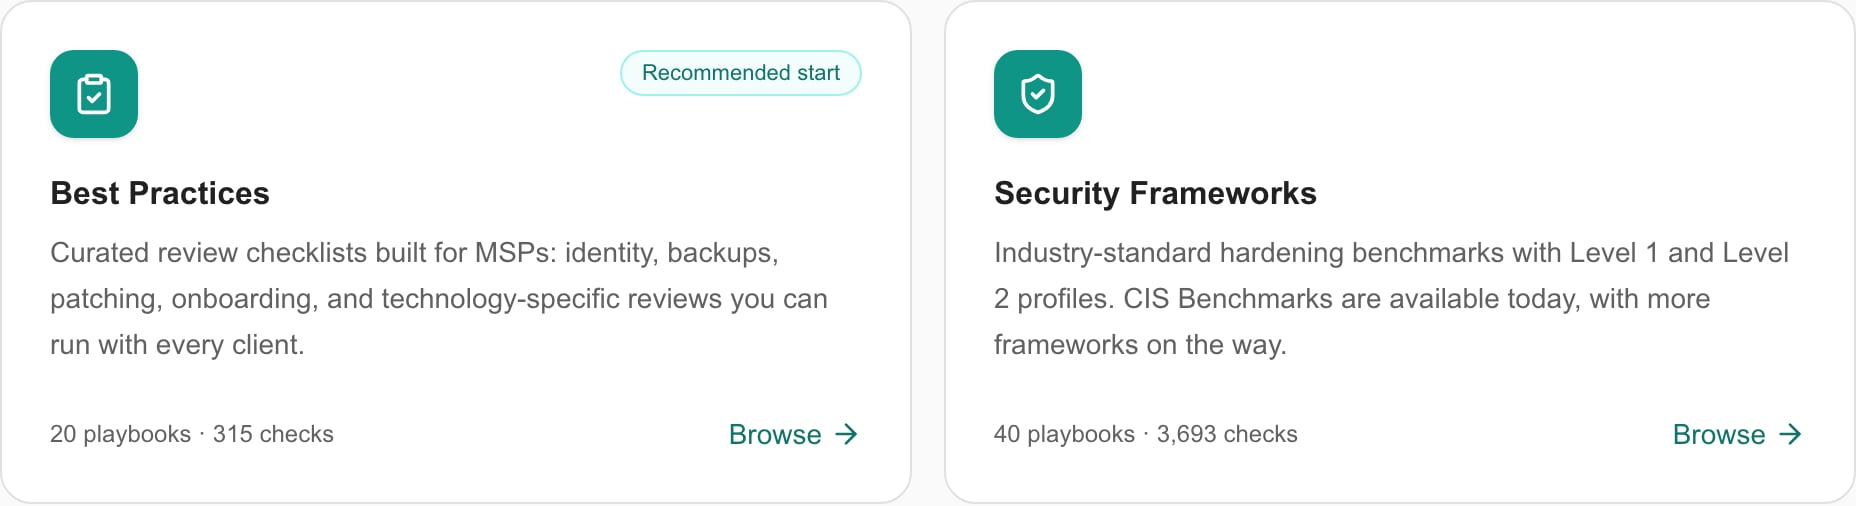
MSP example: the released library entry cards. Catalog counts can change.
Move from a playbook to an assessment
- Open the playbook details to read its check list. Close the preview when finished.
- Use Add to review the destination folder, status list and any device-type suggestions.
- Submit Add to Tenant only after reviewing those choices. The settings guide explains the distinct immediate Copy action and duplicate-import behavior.
- Inspect the imported group and checks under Settings > Compliance. Tailor guidance and applicability to the intended review.
- Add the relevant group or checks to the appropriate run/template and company scope using Compliance settings.
- Perform the assessment, record evidence and review the results in Compliance.
Keep copied content current
Track which catalog version you imported and review later changes before creating another copy. The Imported badge helps identify prior imports, but a missing badge is not sufficient reason to repeat an uncertain operation. Inspect the tenant library if a previous import’s result is unclear. Use Adding CIS Benchmarks when selecting CIS product families and L1/L2 variants. Keep benchmark profiles distinct from CIS Controls Implementation Groups. Use Adding NIS2 playbooks for clients subject to the EU NIS2 directive.Troubleshooting
If you can browse but cannot import, ask an MSP administrator to check the relevant management permission and billing. If a check group exists but a company has no assessment, review run/company assignment. If results appear incomplete, inspect actual assessment status and evidence rather than treating the imported check count as completed work.FAQs
Is a playbook a completed assessment?
Is a playbook a completed assessment?
No. It supplies check content. Assign the review, perform the assessment and record evidence separately.
Can Company users import playbooks?
Can Company users import playbooks?
This is an MSP settings workflow. Company users read the assessments shared by their IT provider.
Does importing change endpoint configurations?
Does importing change endpoint configurations?
No. Import adds tenant check content and associated groups; provider remediation is a separate workflow.
Are every framework and latest benchmark always available?
Are every framework and latest benchmark always available?
Use the actual catalog shown in your account, including its product names and versions.
Does an imported group automatically give every company a completed review?
Does an imported group automatically give every company a completed review?
No. Verify the intended company/run assignment and actual assessment results.